Critical PHP Vulnerabilities 2026: What Organizations Should Do Now
Two critical security vulnerabilities in PHP prompted urgent action worldwide on October 21, 2026. Under certain conditions, attackers could exploit these flaws to remotely execute malicious code on affected web servers without authentication. Some organizations temporarily took their websites and applications offline as a precaution.
The incident demonstrates how quickly organizations may need to respond to newly discovered IT security risks. But which PHP versions are affected? What measures should businesses take? And how can organizations ensure that the right IT personnel are informed in time?
What should organizations do now?
Identify affected PHP installations, apply the security updates released on October 21, 2026, and prioritize internet-facing systems. If immediate updates are not possible, additional protective measures should be considered. When urgent changes to business-critical systems are required, the responsible IT teams and decision-makers should be involved without delay.
Over 20 years of experience in alerting
IT alerting, fire alerts, alerting company first responders and much more. ISO-certified server infrastructure. Used by SMEs, corporations, authorities and public organizations.
What Happened with the PHP Vulnerabilities?
On October 20, 2026, the PHP security team announced an unscheduled security release to address two critical vulnerabilities. The updates were published on October 21.
The vulnerabilities, identified as CVE-2026-109618 and CVE-2026-109619, each received a CVSS v4.0 severity score of 9.2. Both can potentially enable remote code execution (RCE). This means attackers may be able to execute malicious code on a vulnerable server over the network.
What makes these vulnerabilities particularly serious is that exploitation may be possible without authentication. PHP installations handling web requests are affected, including systems using PHP-FPM, Apache with mod_php, php-cgi, FrankenPHP and LiteSpeed.
The official PHP security advisory therefore strongly recommends installing the available security updates immediately.
Which PHP Versions Are Affected?
Security updates were released on October 21 for the supported PHP branches:
| PHP version | Security update version |
|---|---|
| PHP 8.5 | 8.5.12 |
| PHP 8.4 | 8.4.27 |
| PHP 8.3 | 8.3.36 |
| PHP 8.2 | 8.2.35 |
Older PHP versions may also be affected. PHP 8.1, for example, is no longer supported by the PHP project. Organizations using older versions may need to upgrade to a supported release or check whether their vendor provides suitable security fixes.
Important: Linux distributions and long-term support vendors may backport security patches to older package versions. The displayed PHP version alone may therefore not be sufficient to determine whether an installation is protected.
Organizations should work with their IT department or hosting provider to identify the PHP versions in use and confirm that the necessary security updates have been applied.
Why Were Websites Temporarily Taken Offline?
The discovery of a critical security vulnerability does not automatically mean that a system has already been attacked. However, operators may need to implement immediate protective measures to reduce the risk of exploitation.
That was the case with the PHP vulnerabilities disclosed in October 2026. Between the initial security warning and the release of the updates, organizations had to decide whether affected applications could safely remain online.
The Swiss hosting provider cyon, for example, temporarily took several hosting services offline on October 21 as a precaution. Once the necessary security updates had been installed and verified, the services were gradually brought back online.
This example highlights an important challenge: Fixing the technical issue is only one part of the response. Organizations must also clarify responsibilities, assess potential business disruptions and keep the relevant people informed.
How Should Organizations Respond to the PHP Vulnerabilities?
1. Identify Affected PHP Systems
The first step is to identify which websites, applications and servers use PHP. In addition to publicly accessible websites, customer portals, administration interfaces and other web applications may also be affected.
IT teams should verify the PHP versions and server configurations in use and determine which systems are accessible from the internet. Systems with the greatest exposure should be prioritized for further investigation and remediation.
2. Apply Security Updates and Protective Measures
The available PHP security updates should be installed as quickly as possible, following the recommendations of the PHP project and the relevant software or hosting providers.
If immediate updates are not possible, temporary protective measures may be necessary. These could include restricting external access or temporarily shutting down affected services.
However, such measures do not replace the necessary security updates. If there is reason to believe that a vulnerability has already been exploited, organizations must also investigate whether the affected system has been compromised.
3. Alert the Responsible IT Teams
Not every security warning requires an immediate alert. However, when business-critical systems are affected, urgent shutdowns become necessary or action is required outside normal working hours, reaching the right people quickly becomes essential.
Depending on the situation, the following roles may need to be involved:
| Responsible team or role | Main responsibility |
|---|---|
| IT Administration and Operations | Identify affected systems and implement technical measures |
| IT Security Team | Assess security risks and coordinate protective measures |
| On-Call IT Team | Handle urgent tasks outside regular business hours |
| IT Emergency Management | Coordinate the organizational response when business operations are significantly affected |
| Affected Business Departments | Receive information about necessary restrictions and operational impacts |
Not everyone needs to be alerted during every security incident. The important point is that organizations define in advance which roles must be involved depending on the severity of the incident and its potential impact on business operations.
4. Track Responses and Coordinate Actions
When urgent notification is required, simply sending a message is not enough. Those responsible also need to know whether the required people are available and who has taken responsibility for the next steps.
A predefined emergency notification process can help involve the right teams and backup personnel without lengthy manual coordination.
It is important to distinguish between acknowledging an alert and completing a technical task. An acknowledgement initially confirms that someone has responded. Whether a security update has been successfully installed must be verified and documented separately.
Practical Example: Alerting IT Teams About a Critical PHP Vulnerability
Imagine a company operating several publicly accessible web applications built with PHP. Its IT security department receives an urgent warning about a critical vulnerability. An initial assessment indicates that a business-critical system may be affected.
Because additional IT personnel must be involved at short notice, a predefined alert scenario is activated.
Example of an internal IT alert:
Critical PHP Vulnerability - Urgent System Review Required
A critical security vulnerability has been reported in PHP. Please review the assigned systems immediately and coordinate any necessary protective measures with the IT security team.
Response required: "Taking responsibility" or "Not available".
Such an alert helps establish a shared understanding of the situation. It also makes it possible to see who has acknowledged the notification and whether additional responsible personnel need to be involved.
The exact process depends on the organization's IT emergency procedures. Alerting does not replace the technical investigation or decisions about appropriate security measures.
What Happens If Internal Communication Systems Fail?
During serious IT incidents, affected systems may need to be shut down temporarily. In some cases, internal communication services may also become unavailable.
Organizations should therefore avoid relying exclusively on internal email distribution lists or manual telephone call lists. Predefined notification procedures using external communication channels can help teams remain reachable when normal systems are unavailable.
The important question is not only how employees communicate under normal conditions, but also which communication channels remain available when parts of the company's IT infrastructure are affected.
Find out how to identify weaknesses in your notification procedures, acknowledgements and escalation paths in our guide to reviewing alerting workflows.
How Can safeREACH Support Organizations During Critical IT Security Incidents?
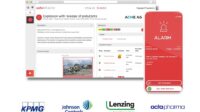
With the safeREACH emergency notification system, organizations can prepare alert scenarios for critical IT incidents in advance.
When necessary, on-call IT teams, administrators and other responsible personnel can be notified immediately. Responses can be tracked centrally, making it possible to see who has acknowledged an alert. Notifications can be triggered manually or automatically through connected IT monitoring systems, provided the required integration has been configured.
The cloud-based emergency notification system supports alerting through available external communication channels, even when internal IT services are unavailable.
Detecting and fixing security vulnerabilities remains the responsibility of qualified IT professionals. safeREACH supports the notification and communication processes between the people involved.
Learn more about IT alerting for outages and incidents.
Conclusion: The PHP Vulnerabilities Show Why Preparation Matters
The two critical PHP vulnerabilities disclosed in October 2026 demonstrate how quickly organizations may need to respond to newly identified security risks. Even precautionary measures can create significant organizational challenges, regardless of whether a cyberattack has actually occurred.
Installing the appropriate security updates promptly remains the most important technical measure. At the same time, organizations should ensure that the right people can be reached, decisions can be coordinated and necessary actions can begin without unnecessary delays.
A predefined IT alerting process can help organizations achieve exactly that.
The safeREACH emergency notification system itself does not use PHP and was not affected by these vulnerabilities. Our company website uses PHP and has already been updated. Further details are available in our dedicated product news 'Critical PHP Security Vulnerabilities: safeREACH Not Affected'.
Ready to reduce response time in critical situations?
Start using a professional emergency notification system that enables fast alerting, clear escalation paths and full transparency during incidents.
Be prepared before the next disruption occurs.